What Is a SOAR Tool, and Why Does Every Security Team Want One?
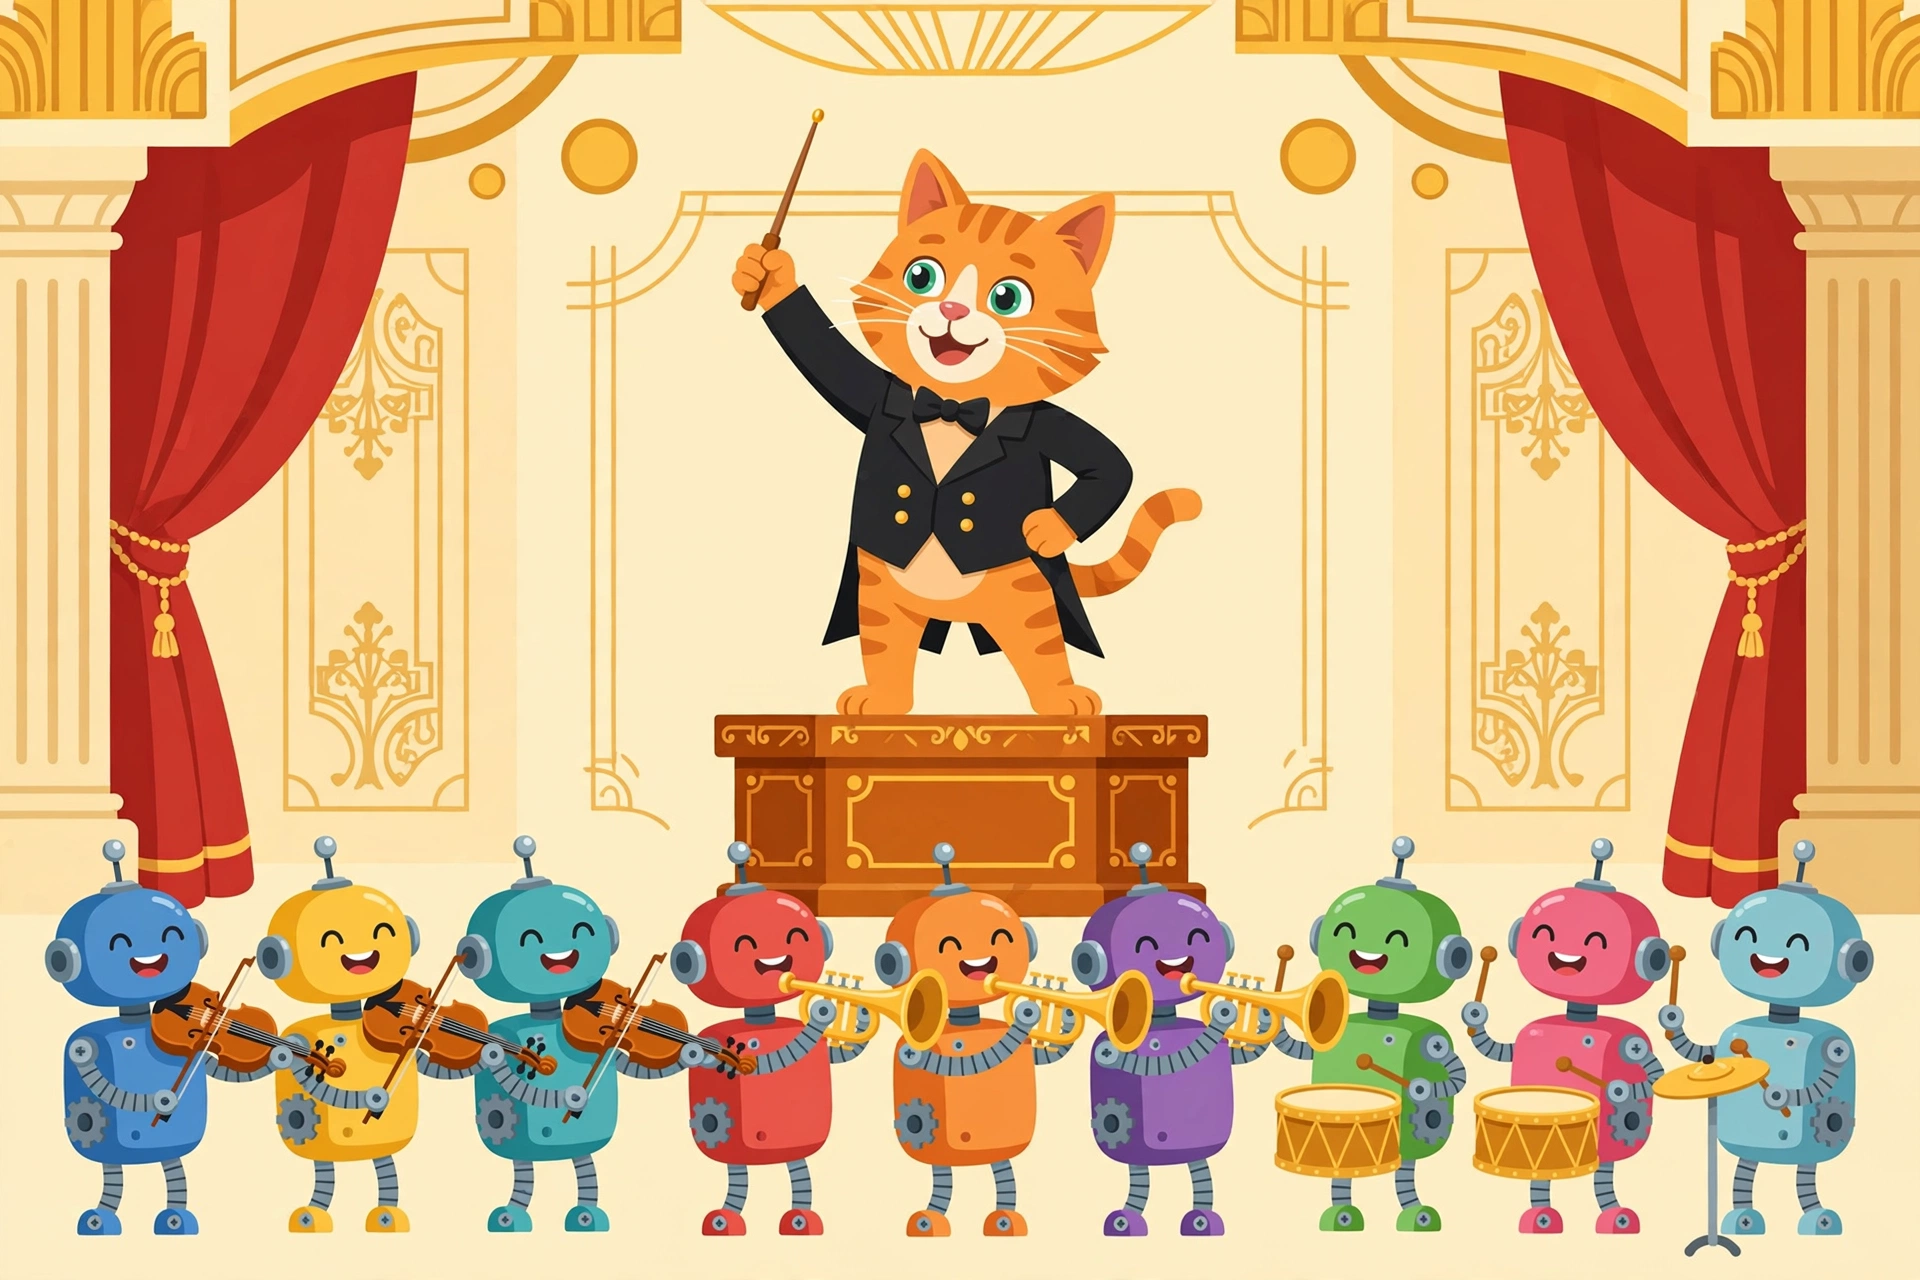
The cat conductor and his robot orchestra. One baton, many players, zero missed cues. That's SOAR.
Picture an orchestra
Now replace the conductor with a cat, and every musician with a robot. The cat raises the baton. The robots play — violins, trumpets, drums — every cue hit, every note on time, at a speed no human orchestra could match.
That image is the entire idea behind a SOAR tool. Here's the breakdown, with zero jargon.
The problem: too many alarms, not enough humans
A company's security team — the SOC, or Security Operations Center — watches over thousands of laptops, servers, and accounts. All of them are constantly shouting "something happened!" An employee clicked a weird link. A laptop talked to a strange server. Someone logged in at 3 AM.
Most of those shouts are nothing. A few are real break-ins. And humans have to tell the difference.
Imagine 10,000 fire alarms going off every day, and you're the only firefighter. By alarm 200, you've stopped running. By alarm 2,000, you miss the real fire. Security people call this alert fatigue — and it's the reason good analysts burn out and real attacks slip through.
SOAR, word by word
SOAR stands for Security Orchestration, Automation, and Response. Four words, each doing work:
- Security — the world it lives in. This is all about defending computers and networks.
- Orchestration — the conductor part. A company owns dozens of security tools: email filters, firewalls, laptop agents, threat-intelligence feeds. Left alone, they don't talk to each other. Orchestration connects them so one alert can trigger actions across all of them at once — like the conductor cueing every section with a single wave of the baton.
- Automation — the robot musicians. The boring, repetitive steps get written down once as a playbook, and then the playbook runs itself every single time. No coffee breaks.
- Response — the key difference from tools that only watch. A SOAR doesn't just send an email saying "something looks bad." It does something: quarantines the laptop, blocks the malicious address, opens a ticket.
If you can describe the response as a recipe — when X happens, do Y, then Z — a SOAR can conduct it. If it needs judgment, a human still holds the baton.
A day in the life
9:04 AM: an employee reports a phishing email.
Without SOAR, an analyst spends 45 minutes on it: open the email, extract the links, check each link against threat lists, search for who else received it, delete it from every inbox, block the sender.
With SOAR, a playbook does all of that in about two minutes — no human touched it. The analyst only gets involved for the one weird case the playbook couldn't classify. Multiply that by hundreds of reports a week, and you start to see why teams want one.
Why every team wants one
- Speed. Machines respond in seconds. Attackers move in minutes. Humans move… after coffee.
- Scale. 10,000 alarms are fine when robots check the boring 9,990 and humans see the interesting 10.
- Consistency. The playbook does it the same way at 3 AM as at 3 PM. Humans get tired. Playbooks don't.
- Humans do human work. Freed from the assembly line, analysts spend time on judgment, threat hunting, and the strange cases — the stuff that's actually fun.
What it's not
It's not magic AI that "hacks back." It doesn't replace analysts — it decides which 10 alarms out of 10,000 deserve a human. And the golden rule: garbage in, garbage out. A bad playbook just automates bad decisions faster. Someone smart still has to write the music.
Try it yourself
Pick one annoying, repetitive thing you do on a computer. Now write down the exact steps — precisely enough that a very literal robot could follow them. Congratulations: you just drafted a playbook. That's the whole idea. SOAR just runs yours at 3 AM without complaining.
Next in this series at Level 4: we build a tiny playbook in Python that watches Windows event logs for suspicious logons. Same idea, real code.